Vulnerability Management: Close Security Gaps Systematically
Find, assess and fix security gaps in your IT infrastructure before attackers exploit them. Automate detection and prioritization with OPENVAS.
Book a Free Consultation
Find, assess and fix security gaps in your IT infrastructure before attackers exploit them. Automate detection and prioritization with OPENVAS.
Book a Free ConsultationEvery IT infrastructure has vulnerabilities. The only question is whether your organization finds them first, or an attacker does. Vulnerability management gives you exactly that head start: a continuous process that makes security gaps visible, ranks them by real-world risk and turns them into concrete action.
Vulnerability management is the systematic process organizations use to find security gaps in their IT infrastructure, rank them by severity and fix them in a targeted way. It means taking the perspective of an attacker and checking from the outside which systems, services and applications are genuinely exploitable.
Vulnerability management is more than patch management: patching closes an already known, specific gap, while vulnerability management makes sure that gap gets found and correctly classified in the first place, including cases where no patch exists or a misconfiguration is the real cause. The organizational foundation for this is a working IT security management program, while the page Data Security covers protecting the data itself.
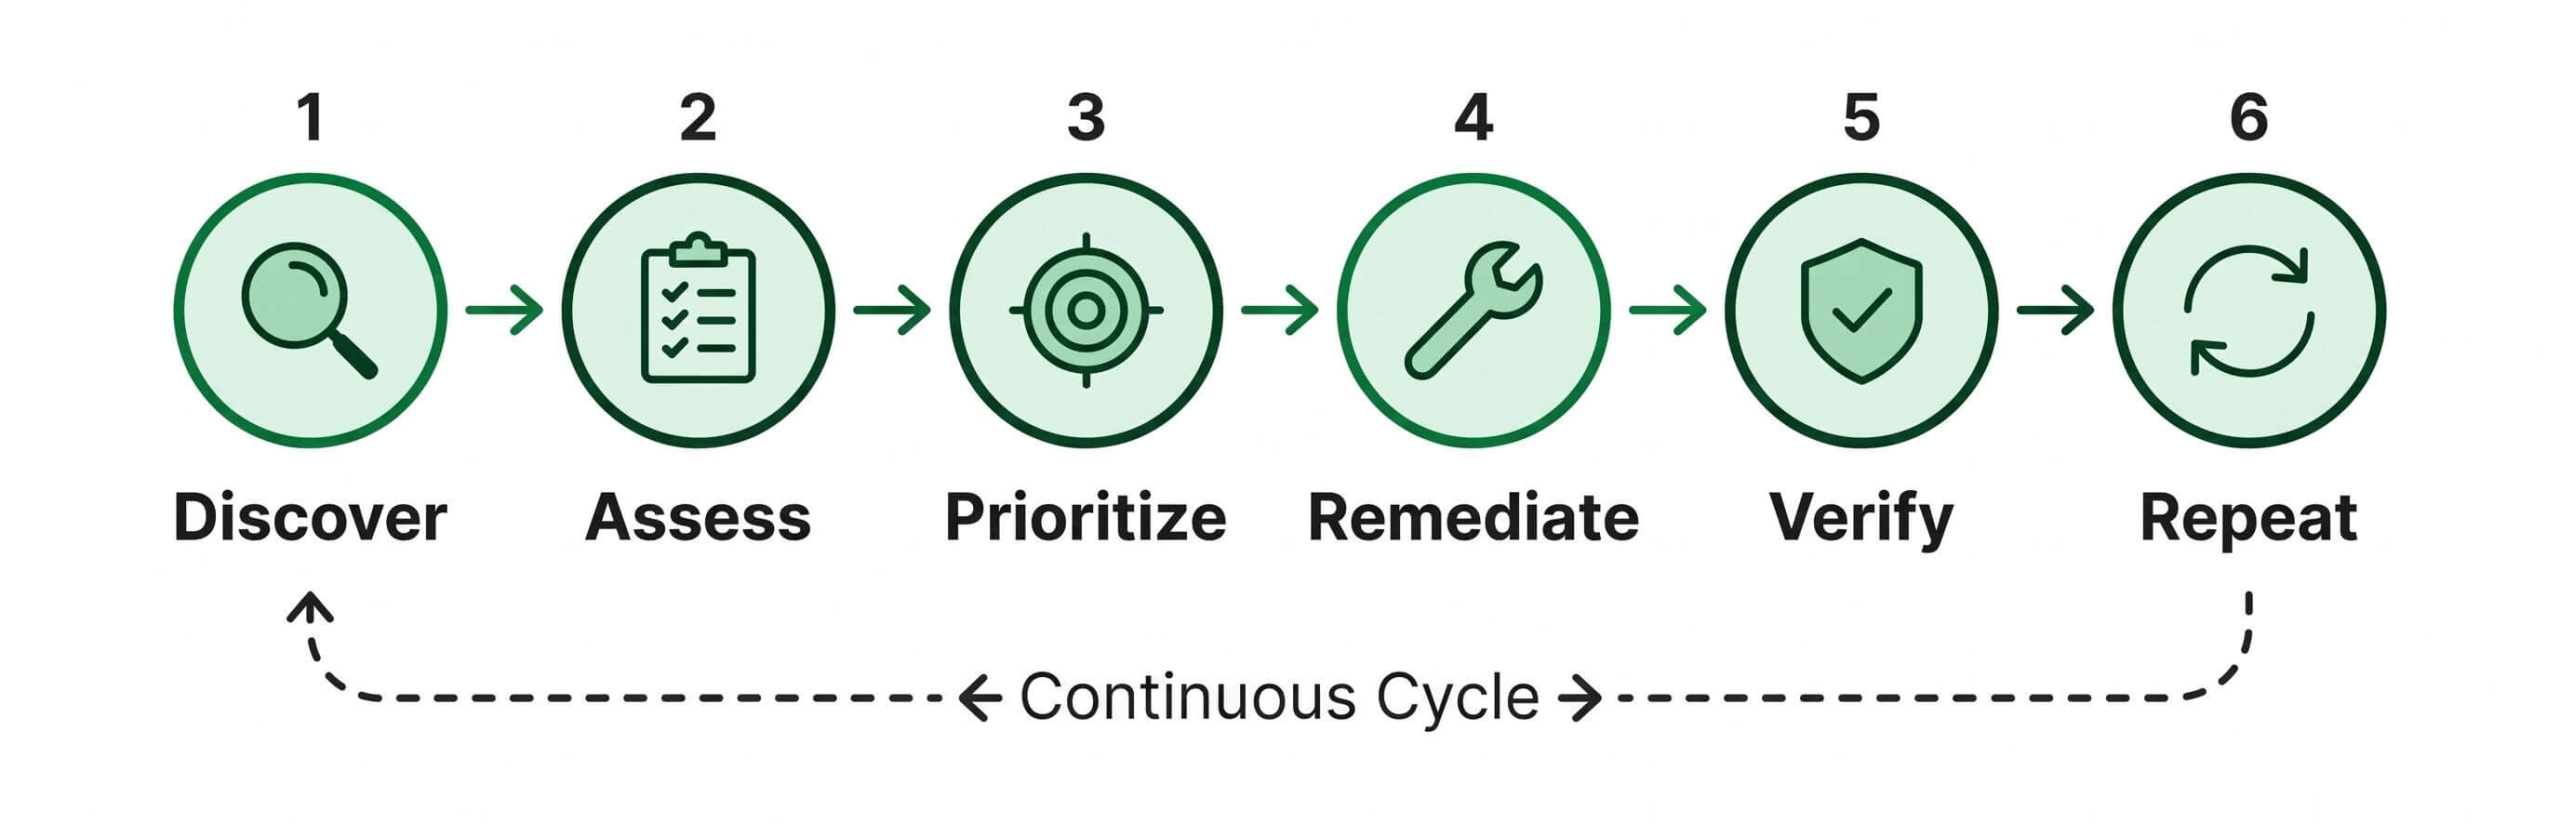
Vulnerability management is not a one-off project. It is a cycle of six steps that keeps repeating:
Current research shows just how wide the gap between disclosure and actual remediation often is:
Sources: Edgescan Vulnerability Statistics Report 2025 and 2026; Verizon Data Breach Investigations Report 2025.
No organization can fix every vulnerability at once. Three factors decide which gap gets closed first:
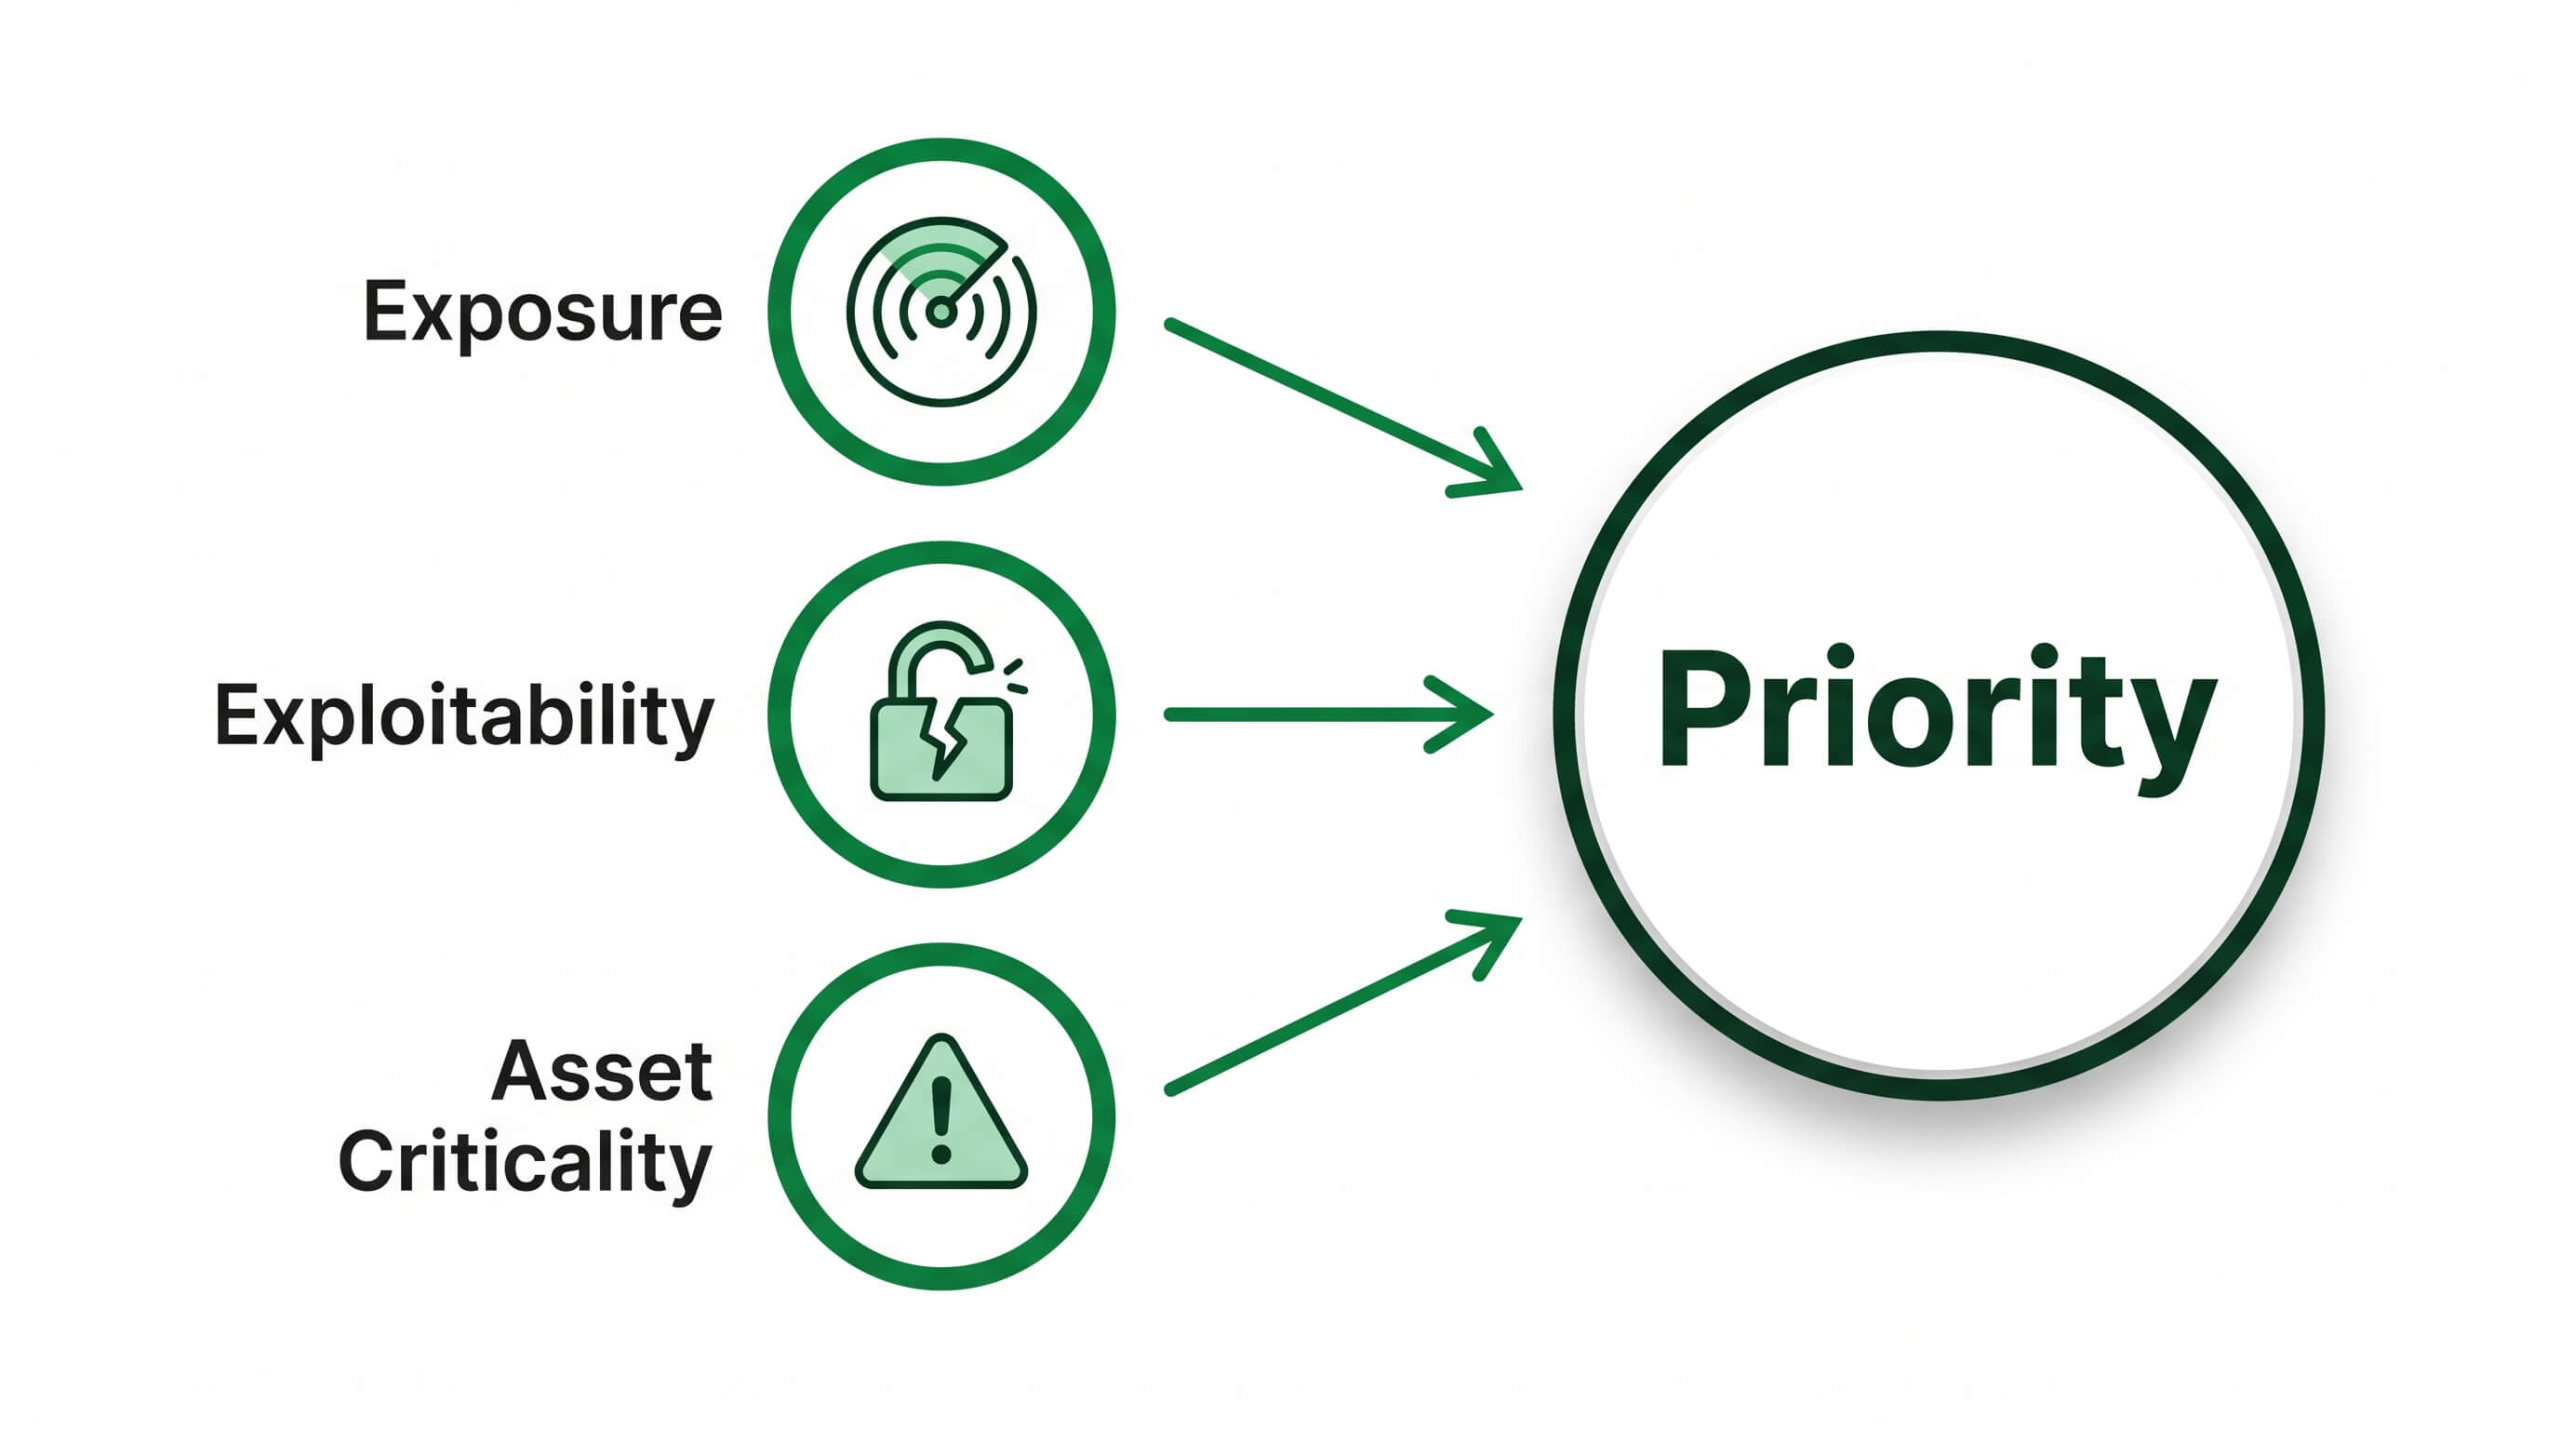
Patching still matters, but it does not replace vulnerability management: some gaps simply have no patch, others cannot be updated because of a business-critical application, and misconfigurations such as a weak admin password appear regardless of how current your patch level is.
The three terms are often confused, but they complement rather than replace one another:
| Area | Focus | Frequency | Typical Output |
|---|---|---|---|
| Vulnerability Management | Systematically finding, assessing and fixing all vulnerabilities | Continuous, updated daily | A prioritized list with recommended actions |
| Patch Management | Deploying available updates for already known gaps | Follows the vendor's patch cycle | An updated software version |
| Penetration Testing | A targeted, manual attack attempt on selected systems | Point-in-time, usually once or twice a year | A detailed report on concrete attack paths |
If you are specifically interested in a transparent, openly viewable scanner core, the page Open Source Vulnerability Management covers the benefits and limits of that approach in detail.
ISO/IEC 27001:2022 does not just imply vulnerability management, it requires it through a dedicated control: Annex A 8.8, “Management of Technical Vulnerabilities” (carried over from Annex A 12.6.1 in the 2013 version of the standard). The control obliges certified organizations to obtain timely information about technical vulnerabilities in the systems they use, assess their own exposure and take appropriate remediation measures.
What matters to auditors is less the specific tool and more the evidence of a working process: a current asset inventory, a documented scan frequency, traceable prioritization and proof of remediation deadlines being met. OPENVAS generates exactly this evidence automatically, from initial detection through CVSS scoring to the verification scan after remediation.
Vulnerability management scales with company size, not just upward:
OPENVAS tests your network and every connected device against more than 100,000 vulnerability tests in the OPENVAS ENTERPRISE FEED, which is updated several times a day. You get an up-to-date view of your security posture, including severity and a recommended action for every finding.
A concrete starting point for building a structured vulnerability management practice:
What is vulnerability management?
Vulnerability management is the ongoing process of finding security gaps in IT systems, ranking them by severity and fixing them in a targeted way, rather than checking for them once.
How does vulnerability management differ from patch management?
Patch management deploys available updates for already known gaps. Vulnerability management finds and assesses those gaps in the first place, including cases where no patch exists or a misconfiguration is the actual cause.
How often should an organization scan?
Since new vulnerabilities appear every day, scans should run continuously rather than once. Critical, internet-facing systems benefit from daily scans, while internal systems often work well on a weekly cycle.
What do CVSS and EPSS mean?
CVSS rates how severe a vulnerability is in theory. EPSS adds an estimate of how likely it is to actually be exploited in the coming days, which sharpens prioritization.
What does vulnerability management from Greenbone cost?
OPENVAS BASIC starts at €2,524 per year as an entry-level solution for small businesses. OPENVAS SCAN is priced based on the environment being scanned and is calculated individually on request.
Which company sizes benefit from vulnerability management?
All of them: small businesses with just a handful of IP addresses benefit just as much as large enterprises and public agencies with many sites and complex reporting duties.
What does ISO 27001 require for vulnerability management?
ISO 27001:2022 requires certified organizations, through Annex A Control 8.8, to identify technical vulnerabilities in a timely manner, assess their own exposure and implement appropriate countermeasures. Auditors mainly check the asset inventory, scan frequency and documented remediation deadlines.
What role does vulnerability management play in NIS2 and the Cyber Resilience Act?
Both frameworks require affected organizations to actively manage vulnerabilities in their systems and products and to document incidents in a traceable way. Continuous vulnerability management provides the technical foundation for that.
How is this different from open source vulnerability management?
Vulnerability management describes the general process, regardless of the tool used. Open source vulnerability management additionally focuses on a transparent, openly viewable scanner core. Read more on the page Open Source Vulnerability Management.
Let us check together where your IT infrastructure stands today and what a vulnerability management process tailored to you could look like.