
ISO 27001ISO 9001Developed in EuropePowering the world's most widely used open source vulnerability scanner
Wait on a single source, and you are already behind.
The window between disclosure and the first attack keeps getting shorter. Attackers increasingly use AI to exploit vulnerabilities faster. Public databases, meanwhile, often lag behind, and some now fully process only a fraction of new entries. That is why we go straight to vendor and security advisories. A test can be ready for you before the vulnerability even shows up in a public database.
Fast. Precise. Sovereign.

Fast
Where quality allows, tests are generated through supervised automation, straight from primary sources. That frees our experts to focus on the complex cases. For systems you have already scanned, OPENVAS can surface new vulnerabilities without a rescan. So you know where you stand while others are still waiting for a database entry.

Precise
We keep false positives low with active tests wherever possible. They send a safe test payload and check whether your system responds the way a vulnerable one would. That settles cases where version or configuration data alone would leave doubt. Every finding comes with a Quality of Detection score that shows how reliable it is, and active tests score highest. You set the threshold for what makes it into your reports.

Sovereign
The OPENVAS ENTERPRISE FEED is developed in Europe. It draws on vulnerability intelligence from around the world: the leading US databases, ENISA, the European Union Agency for Cybersecurity, and the vendors themselves. So you never depend on a single source. Every test is signed, so you know it comes from Greenbone, unaltered.
From finding to priority
Not every vulnerability is equally urgent. For every finding, the OPENVAS ENTERPRISE FEED answers three questions: How severe is it (CVSS)? How likely is it to be exploited (EPSS)? How reliable is the detection (Quality of Detection)? You add the fourth: what role the affected system plays in your organization. A server holding customer data needs attention sooner than a test machine in the lab. The result is a priority you can trace and justify to auditors.
From the OPENVAS ENTERPRISE FEED
From your environment
How does this fit your environment? Let's look at it together.
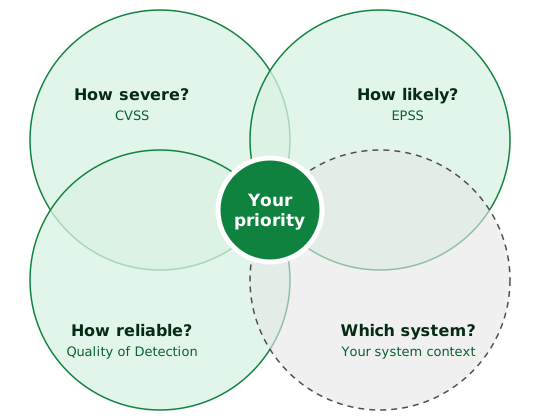
CVSS and EPSS are open standards maintained by FIRST, the Forum of Incident Response and Security Teams.
COMMUNITY FEED vs. ENTERPRISE FEED
The OPENVAS ENTERPRISE FEED includes every test in the COMMUNITY FEED, then adds coverage for enterprise software, compliance checks and EPSS-based prioritization. With OPENVAS SCAN, you also get direct access to our experts.
| Feature | COMMUNITY FEED Included in OPENVAS FREE |
ENTERPRISE FEED Included in every OPENVAS product from BASIC up |
|---|---|---|
| Enterprise software and network gear (e.g., Cisco, Microsoft Exchange, Palo Alto Networks) | ✕ | ✓ |
| Compliance checks against CIS Benchmarks | ✕ | ✓ |
| EPSS-based prioritization | ✕ | ✓ |
| Enterprise Support with contractual response times (with OPENVAS SCAN) | ✕ | ✓ |
| Access to Greenbone Professional Services (on request) | ✕ | ✓ |
| Widely used standard software and operating systems (e.g., Microsoft Office, Ubuntu Linux) | ✓ | ✓ |
| BSI IT-Grundschutz checks (the security baseline of Germany’s Federal Office for Information Security) | ✓ | ✓ |
| Explore OPENVAS FREE | Talk to an expert |
Support you can count on
With OPENVAS SCAN, the OPENVAS ENTERPRISE FEED comes with direct access to our Enterprise Support, plus our Professional Services whenever you need them.

Support from Europe
Our support team is based in Europe and works with you directly.

Real product experts
Your request goes to people who know OPENVAS inside out and work with it every day.

Committed response times
When something critical comes up, every hour counts. Your contract sets out our response times.
Tests for the software your business runs on
A selection of vendors whose products the OPENVAS ENTERPRISE FEED covers.
Amazon (AWS)CiscoIBMSAPDellHPEBroadcomSiemensVMwareCitrixPalo Alto NetworksF5FortinetTrend MicroCheck PointSophosOpenTextAtlassianSplunk
Frequently asked questions about the OPENVAS ENTERPRISE FEED
What is the OPENVAS ENTERPRISE FEED?
The OPENVAS ENTERPRISE FEED is the collection of vulnerability tests OPENVAS uses to check your IT systems. Greenbone builds these tests from vulnerability sources around the world and keeps the feed continuously updated. It includes every test in the COMMUNITY FEED and adds coverage for enterprise software, compliance checks and EPSS-based prioritization. With OPENVAS SCAN, you also get access to Enterprise Support.
How does the COMMUNITY FEED differ from the ENTERPRISE FEED?
The OPENVAS ENTERPRISE FEED includes every test in the COMMUNITY FEED. On top of that, it covers enterprise software and network gear, such as Cisco, Microsoft Exchange or Palo Alto Networks. It also includes compliance checks against CIS Benchmarks and EPSS-based prioritization. With OPENVAS SCAN, you also get access to Enterprise Support.
Is the COMMUNITY FEED free?
Yes. The COMMUNITY FEED is free and gives you basic coverage to get started with OPENVAS. Tests for enterprise software and compliance checks come with the OPENVAS ENTERPRISE FEED, which is included in every OPENVAS product from BASIC up.
How often is the OPENVAS ENTERPRISE FEED updated?
Greenbone keeps the OPENVAS ENTERPRISE FEED continuously updated. When your systems apply the updates is up to your configuration.
Where does the information for new tests come from?
Greenbone draws on vulnerability intelligence from around the world: the leading US databases, ENISA, the European Union Agency for Cybersecurity, plus vendor advisories and security bulletins. Because we evaluate vendor advisories directly, a test in the OPENVAS ENTERPRISE FEED can be ready before a vulnerability appears in a public database.
What if public databases do not fully process a vulnerability?
Some public databases now fully process only a fraction of new vulnerabilities. That is why the OPENVAS ENTERPRISE FEED draws on vulnerability intelligence from around the world: the leading US databases, ENISA, vendor advisories and security bulletins. Your vulnerability management never hinges on a single source.
Does Greenbone use AI to develop tests?
Yes. Depending on complexity, tests for the OPENVAS ENTERPRISE FEED are built through supervised automation, with the help of supervised AI, or through research by Greenbone’s security experts.
How does the OPENVAS ENTERPRISE FEED keep false positives low?
Wherever possible, Greenbone uses active tests. They send a safe test payload and check whether the system responds the way a vulnerable one would, which settles cases where version or configuration data alone would leave doubt. Every finding also comes with a Quality of Detection score showing how reliable it is, with active tests scoring highest, and you set the threshold for what appears in your reports.
How do I decide which vulnerabilities to fix first?
For every finding, the OPENVAS ENTERPRISE FEED provides three values: CVSS for severity, EPSS for the likelihood of exploitation and Quality of Detection for the reliability of the detection. Combine them with the role of the affected system in your organization, and you have your priority.
Where is the OPENVAS ENTERPRISE FEED developed?
The OPENVAS ENTERPRISE FEED is developed by Greenbone in Europe. Every test is signed, so you know it comes from Greenbone, unaltered.
How do I get the OPENVAS ENTERPRISE FEED?
The OPENVAS ENTERPRISE FEED is included in every OPENVAS product from BASIC up. Talk to us, and we will help you find the right product for your environment.
Ready to get ahead?
Tell us about your environment, and we will help you find the solution that fits.